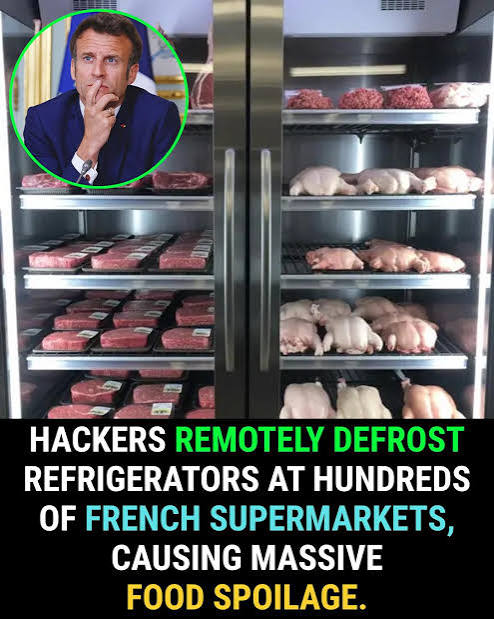

From supermarket freezers to power networks, security systems and critical infrastructure, a frightening new frontier in cyber warfare is emerging. Are governments and security agencies losing the race against increasingly sophisticated hackers?
ABT NEWS | TECHNOLOGY, SECURITY & GLOBAL AFFAIRS |
Imagine walking into your local supermarket tomorrow morning only to discover that its refrigerators have been remotely switched off, its freezers have been heated to 50°C, millions of pounds’ worth of food have become unsafe, and nobody knows who is responsible.
This is no longer a frightening science-fiction scenario. It is happening in Europe.
In what could be a disturbing warning of the next generation of cyber warfare, hackers have reportedly infiltrated supermarket refrigeration systems, remotely manipulated temperatures and caused widespread destruction of food stocks.
And the most frightening question is not simply how they did it.
It is: WHAT ELSE CAN THEY TAKE CONTROL OF?
THE REFRIGERATOR ATTACK: A WAKE-UP CALL FOR THE WORLD
On 2 November 2026, Reuters reported a fresh wave of cyberattacks affecting supermarket refrigeration systems across Europe.
Retailers in Belgium, Luxembourg, Sweden and Ireland reported disruptions, with incidents also reported in other European countries.
Among the affected businesses were supermarket groups Ahold Delhaize, Colruyt, ICA, Coop and Carrefour, as well as IKEA stores.
In one Swedish supermarket, refrigerators and freezers reportedly reached temperatures of 50°C.
The consequences were devastating. Food had to be removed from shelves and discarded, while businesses faced financial losses and disruption.
In Ireland, SuperValu confirmed that refrigeration systems in 13 of its 223 stores had been affected.
These incidents followed an attack in France in October, where hackers reportedly manipulated cooling systems in hundreds of supermarkets, resulting in food losses estimated at tens of millions of euros and reports of fires.
The Guardian also reported that some affected refrigeration controllers had remained accessible through the internet despite earlier warnings about vulnerabilities.
This is the extraordinary reality of our increasingly connected world: a criminal sitting thousands of miles away may be able to interfere with equipment that controls the temperature of food in a supermarket.
And the implications extend far beyond groceries.
THIS IS NOT JUST ABOUT HACKERS BREAKING INTO COMPUTERS
For years, the public understanding of cybercrime has largely revolved around stolen passwords, hacked bank accounts, compromised social media profiles and ransomware attacks.
But the threat is evolving.
Modern buildings, factories, hospitals, supermarkets, transport networks and energy facilities increasingly depend on internet-connected equipment.
These systems are collectively associated with what cybersecurity specialists call the Internet of Things (IoT) and Operational Technology (OT).
They include:
- Refrigeration and industrial cooling systems.
- Electricity and power distribution controls.
- Water treatment and pumping systems.
- Hospital equipment and building management systems.
- Security cameras, alarms and access-control systems.
- Manufacturing machinery and transport infrastructure.
When these systems are inadequately protected, an attacker may be able to move beyond stealing information and interfere with physical operations.
The refrigerator attacks demonstrate precisely why this matters.
A compromised computer system can cause financial damage. A compromised industrial control system can potentially cause physical damage, disrupt essential services and endanger lives.
The distinction is enormous.
THE WARNING SIGNS ARE ALREADY THERE
This is not an isolated technological curiosity.
In its 2026 threat assessment, the UK’s National Cyber Security Centre (NCSC) warned that it had observed increased targeting of operational technology across multiple sectors globally, including the UK.
It also warned that state and non-state actors were engaging in disruptive cyber activity against critical national infrastructure and other organisations.
The agency assessed that the threat from state use of offensive cyber capabilities had almost certainly increased.
Meanwhile, the European Union Agency for Cybersecurity (ENISA), in its 2026 Threat Landscape report, identified ransomware as the most immediately impactful cyber threat.
It also highlighted the continuing influence of geopolitical tensions, cyber espionage, hacktivism and the growing potential for artificial intelligence to support malicious operations.
In other words, the cyber threat is no longer confined to conventional criminals seeking money.
It can also involve espionage, political intimidation, economic disruption and potentially state-sponsored operations.
THE NUMBERS THAT SHOULD WORRY US
The UK Government’s Cyber Security Breaches Survey 2025/2026 provides another important indication of the scale of the problem.
Its findings include:
- 43% of UK businesses reported experiencing a cyber security breach or attack during the previous 12 months.
- An estimated 612,000 businesses experienced breaches or attacks.
- Approximately 267,000 businesses were estimated to have experienced at least one cybercrime.
- Only 25% of businesses had a formal incident response plan.
These figures reveal a troubling preparedness gap.
Even where attacks are detected, many organisations may not have a sufficiently developed plan for dealing with the consequences.
The report also found that the overall prevalence of cybercrime had remained relatively stable compared with the previous two years.
That qualification matters: the statistics do not establish that every form of cyberattack is increasing.
However, the NCSC’s warning about increased targeting of operational technology suggests that the nature and potential consequences of certain attacks are changing.
ARE SECURITY AGENCIES LOSING THE BATTLE?
There is a difficult question that governments and security agencies must confront.
Why do organisations repeatedly find themselves responding to attacks after damage has already occurred?
Part of the answer lies in the changing nature of the threat.
Traditional security arrangements were developed around identifiable physical boundaries, established communication channels and relatively predictable threats.
Today’s digital infrastructure is interconnected.
A vulnerability in a supplier’s software, a poorly secured remote-access system, an outdated router or an exposed industrial controller can create an entry point into a much larger network.
An attacker does not necessarily need to defeat an entire security system. Sometimes finding one overlooked weakness is enough.
Attribution is another major challenge. Attackers can conceal their identities, operate through compromised devices in different countries and exploit infrastructure belonging to innocent third parties.
This makes identifying, locating and prosecuting perpetrators extraordinarily difficult.
But it would be wrong to suggest that security agencies are completely helpless.
The NCSC, FBI, law enforcement agencies and international cybersecurity organisations have disrupted criminal networks, issued security warnings and helped organisations respond to major incidents.
The real problem is that prevention, intelligence sharing and infrastructure protection must keep pace with an increasingly interconnected threat environment.
WILL WE SEE MORE ATTACKS?
The honest answer is that further attacks are a serious possibility.
Nobody can reliably predict the number or precise targets of future incidents. However, several factors suggest that this threat will remain significant.
1. The expansion of connected technology
Every new remotely managed device potentially creates another point that must be secured.
The problem is particularly serious where equipment has been installed without sufficient cybersecurity planning.
2. Artificial intelligence
AI can help malicious actors automate aspects of reconnaissance, produce convincing fraudulent communications and identify weaknesses more efficiently.
ENISA has specifically warned that emerging AI models are expected to play an increasing role in malicious cyber operations.
3. Geopolitical tensions
Cyber operations can be used to gather intelligence, create disruption or apply pressure without conventional military confrontation.
However, no evidence currently establishes that a particular government was responsible for the supermarket refrigerator attacks.
4. Vulnerable supply chains
Organisations frequently depend on third-party manufacturers, software providers, maintenance contractors and remote-access services.
A weakness in one supplier can expose multiple customers.
5. The economics of cybercrime
Digital attacks can be conducted remotely, sometimes anonymously, and potentially at a fraction of the cost of causing comparable physical disruption.
For attackers, the attraction is obvious: substantial disruption without necessarily having to enter a building.
WHAT CAN BE DONE? THE SOLUTIONS CANNOT WAIT
The response must move beyond issuing statements after every major attack.
Governments, businesses, technology manufacturers and security agencies need a coordinated strategy.
1. Stop exposing critical equipment directly to the internet
The NCSC specifically advises organisations to ensure operational technology is not directly accessible from the public internet.
Remote access must be tightly controlled, monitored and protected.
2. Make cybersecurity compulsory for critical infrastructure
Supermarkets, hospitals, power companies, water providers and transport operators should be subject to enforceable minimum cybersecurity requirements.
Essential equipment must not be treated as ordinary office technology.
3. Introduce mandatory security standards for manufacturers
Manufacturers should provide secure default settings, timely software updates, clear vulnerability reporting procedures and long-term security support.
Devices that cannot receive essential security updates should not remain indefinitely connected to critical networks.
4. Strengthen authentication
Default passwords must be eliminated.
Organisations should implement unique administrator accounts, strong authentication and multi-factor authentication wherever supported.
5. Separate critical systems from ordinary business networks
A hacker who compromises an employee’s computer should not automatically gain access to refrigeration controls, electricity systems or industrial machinery.
Network segmentation can limit the damage when one part of a system is compromised.
6. Establish real-time monitoring and rapid response
Businesses should monitor unusual activity, establish clear incident-response procedures and practise emergency isolation and recovery.
A system that detects suspicious activity at 2am is much more valuable than one that discovers the damage after opening time.
7. Increase international intelligence sharing
Cybercriminals do not respect national borders.
Governments need faster cooperation on threat intelligence, digital evidence, investigations, sanctions and prosecutions.
8. Prepare for physical consequences
Cybersecurity is also a public safety issue.
Supermarkets need independent temperature monitoring and emergency procedures. Hospitals need backup arrangements. Energy and water operators need safe manual operating procedures and tested recovery systems.
The objective must be to ensure that a successful cyberattack does not automatically become a public emergency.
WHAT ABOUT ORDINARY CITIZENS?
The threat is not limited to large corporations.
The FBI has previously warned that compromised internet-connected devices, including streaming equipment, routers and other smart products, can become part of criminal botnets.
In a 2024 joint advisory, the FBI, NSA and other US security agencies described a botnet containing more than 260,000 compromised internet-connected devices as of June that year.
Such networks can be used to conceal attackers’ identities, facilitate attacks and compromise other systems.
Households should therefore:
- Change default passwords on routers and smart devices.
- Install software and firmware updates.
- Avoid downloading applications from untrusted marketplaces.
- Replace unsupported equipment.
- Secure home Wi-Fi networks.
- Use multi-factor authentication on important accounts.
- Disconnect suspicious or unnecessary devices from the network.
The lesson is simple: a smart device should never be assumed to be a safe device merely because it is sold by a recognised retailer.
THE BIGGER QUESTION: ARE WE BUILDING A CONNECTED WORLD THAT WE CANNOT PROTECT?
There is a contradiction at the heart of modern technological development.
We are connecting more equipment, automating more essential services and allowing more systems to be controlled remotely.
Yet security does not always receive the same attention as convenience, efficiency and profitability.
The supermarket refrigerator attacks expose this contradiction in a particularly uncomfortable way.
What happens when the target is not a supermarket but a hospital’s temperature-controlled medicine storage?
What happens when an attacker interferes with a water treatment facility?
What happens when a power distribution system is compromised during a period of extreme weather?
These are questions of national security, economic resilience and public safety.
They are not predictions that these events are inevitable. They are scenarios that responsible governments and infrastructure operators must be prepared to prevent and manage.
ABT NEWS FINAL ANALYSIS: THE NEXT CYBERATTACK MAY NOT LOOK LIKE A CYBERATTACK
The frightening reality is that the next major digital security incident might not begin with a message on your computer screen.
It might begin with a supermarket freezer warming up unexpectedly.
It might begin with a hospital’s building management system malfunctioning.
It might begin with a water facility receiving an unauthorised command.
The public may see the consequences long before they understand that a cyberattack has taken place.
The refrigerator attacks should therefore be treated as more than another technology story.
They are a warning about the vulnerability of the physical infrastructure on which modern society depends.
Security agencies must become more proactive. Governments must demand stronger safeguards. Manufacturers must take responsibility for the products they connect to the internet. Businesses must stop treating cybersecurity as an optional expense.
Because when the digital world controls the physical world, cybersecurity is no longer just about protecting data.
IT IS ABOUT PROTECTING OUR FOOD, OUR WATER, OUR ELECTRICITY, OUR HOSPITALS AND, ULTIMATELY, OUR LIVES.
ABT NEWS: STAY INFORMED. STAY ALERT. STAY SECURE.

 By